Assess Enterprise AI Without Building Your Risk & Control Framework From Scratch.
Practical, audit-ready AI governance tools for Internal Audit, Technology Risk, Compliance, and AI Governance professionals.
32 controls. 3 focused domains. One practical starting point for AI governance assessments.
AI Governance Risk & Control Matrix — Founding Edition
A practical, audit-ready risk and control matrix designed to help Internal Audit, Technology Risk, Compliance, and AI Governance teams identify AI risks, evaluate expected controls, document evidence, and accelerate AI governance assessments.
Instead of starting with a blank spreadsheet and translating multiple AI frameworks into usable controls yourself, the Founding Edition gives you a structured starting point that can be tailored to your organization, AI systems, and risk environment.
Structured AI risks and controls designed to give audit, risk, and governance teams a practical starting point.
AI Governance & Oversight, AI Data & Privacy, and GenAI & LLM Security.
Evidence expectations, audit testing guidance, risk ratings, framework mappings, and tailoring considerations.
Every Control Includes
- Risk Domain
- Risk ID
- Risk Statement
- Control ID
- Control Objective
- Detailed Control Activity
- Illustrative Primary Owner
- Frequency
- Control Nature
- Control Type
- Expected Evidence
- Audit Test Procedure
- NIST AI RMF Mapping
- NIST Generative AI Profile Mapping
- IIA Alignment
- Inherent Risk
- Expected Residual Risk
- Tailoring Notes
Three Domains Built Around Practical AI Risk
AI Governance & Oversight
Governance structure, AI strategy, acceptable use, AI inventory, risk classification, deployment approvals, independent challenge, training, legal/compliance review, third-party governance, periodic review, and decommissioning.
12 controls includedAI Data & Privacy
Data provenance, quality, sensitive data, privacy review, minimization and retention, access, lineage, output leakage, third-party data rights, and material AI data changes.
10 controls includedGenAI & LLM Security
Threat modeling, prompt injection, guardrails, adversarial testing, data leakage, output validation, human oversight, logging, change management, third-party dependencies, and incident response.
10 controls includedMore Than a Checklist
The Founding Edition includes a practical methodology designed to help you move from generic control language to an organization-specific assessment.
Identify the AI system, use case, business process, and assessment boundary.
Identify which controls apply to the technology and risk context.
Adapt control language to the organization’s actual process and operating model.
Identify accountable control owners and responsible functions.
Define evidence appropriate to demonstrate control design and operation.
Tailor and perform the included audit test procedures.
Evaluate inherent and expected residual risk using your approved methodology.
Capture assumptions, exceptions, and tailoring decisions.
Preview the Founding Edition
See the structure, depth, and practical orientation of the AI Governance Risk & Control Matrix.
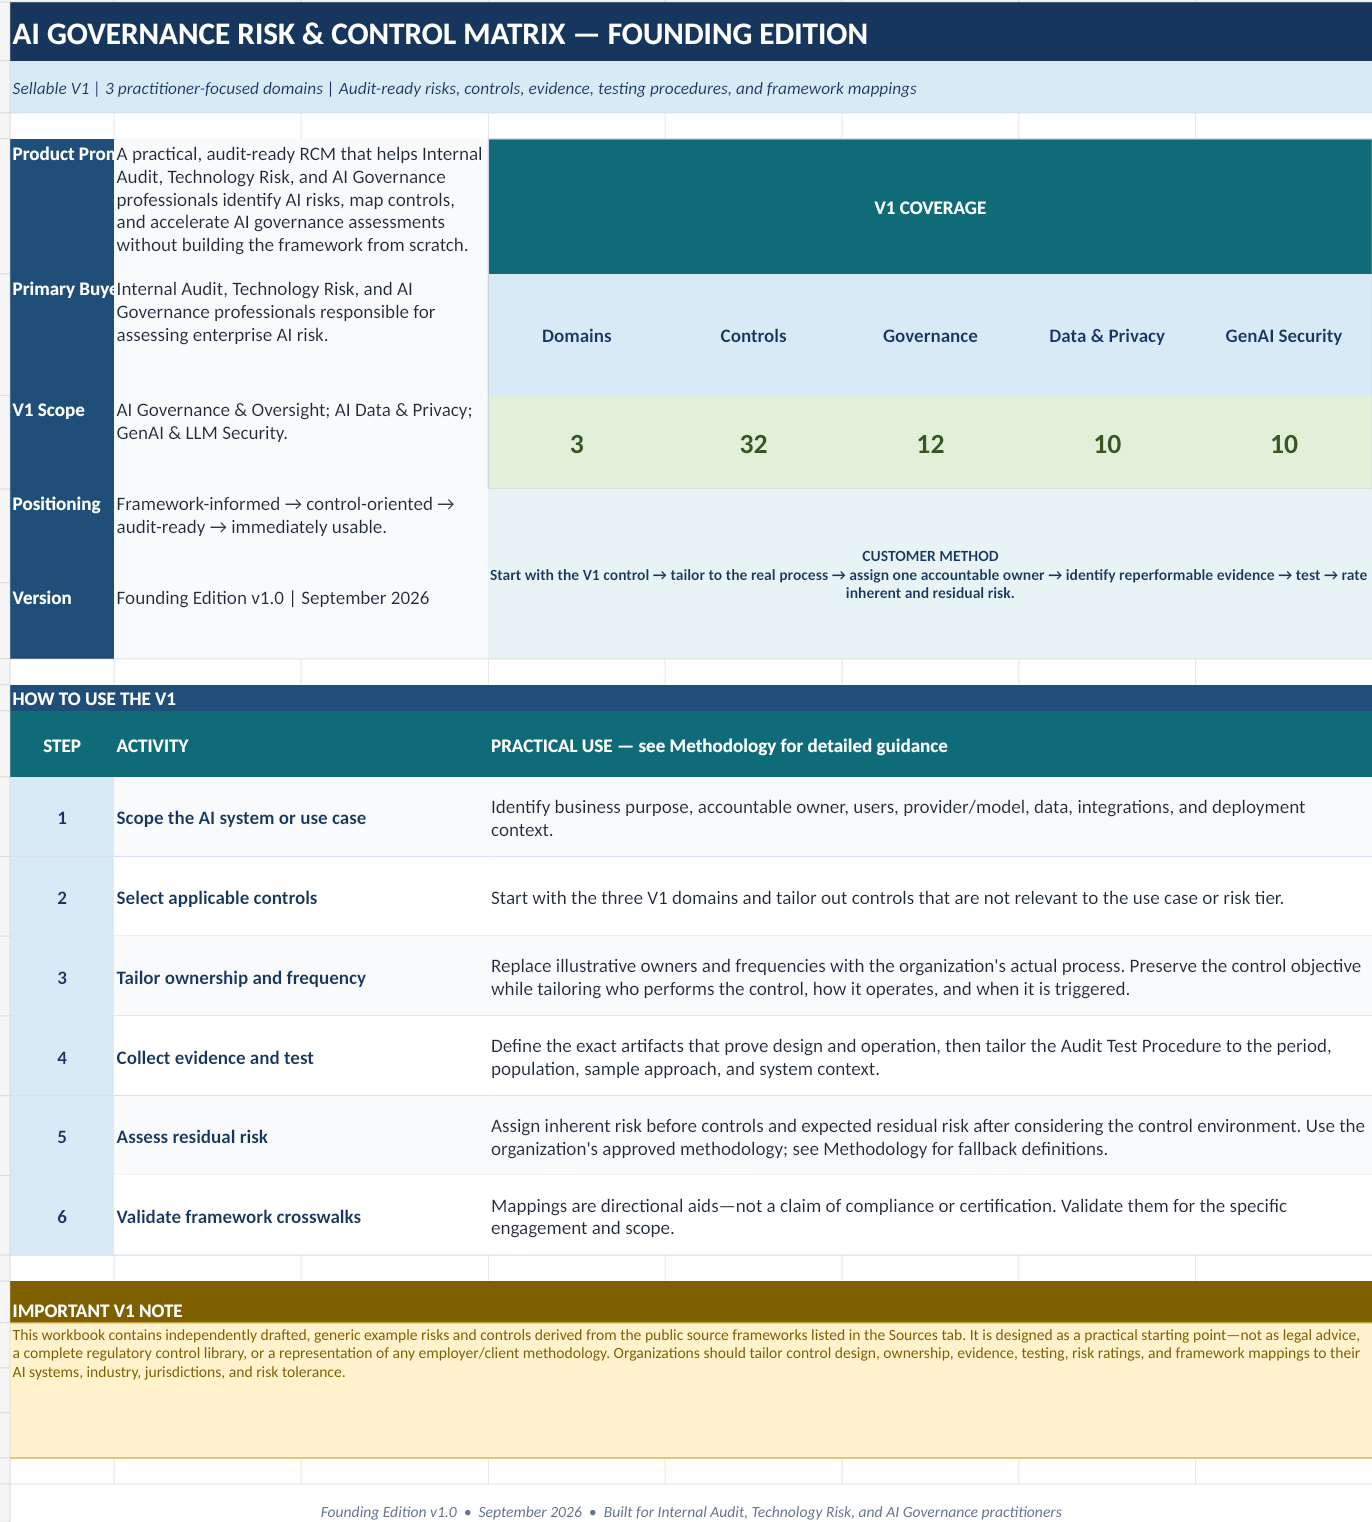 01
START HERE
Product overview, coverage summary, positioning, and step-by-step guidance.
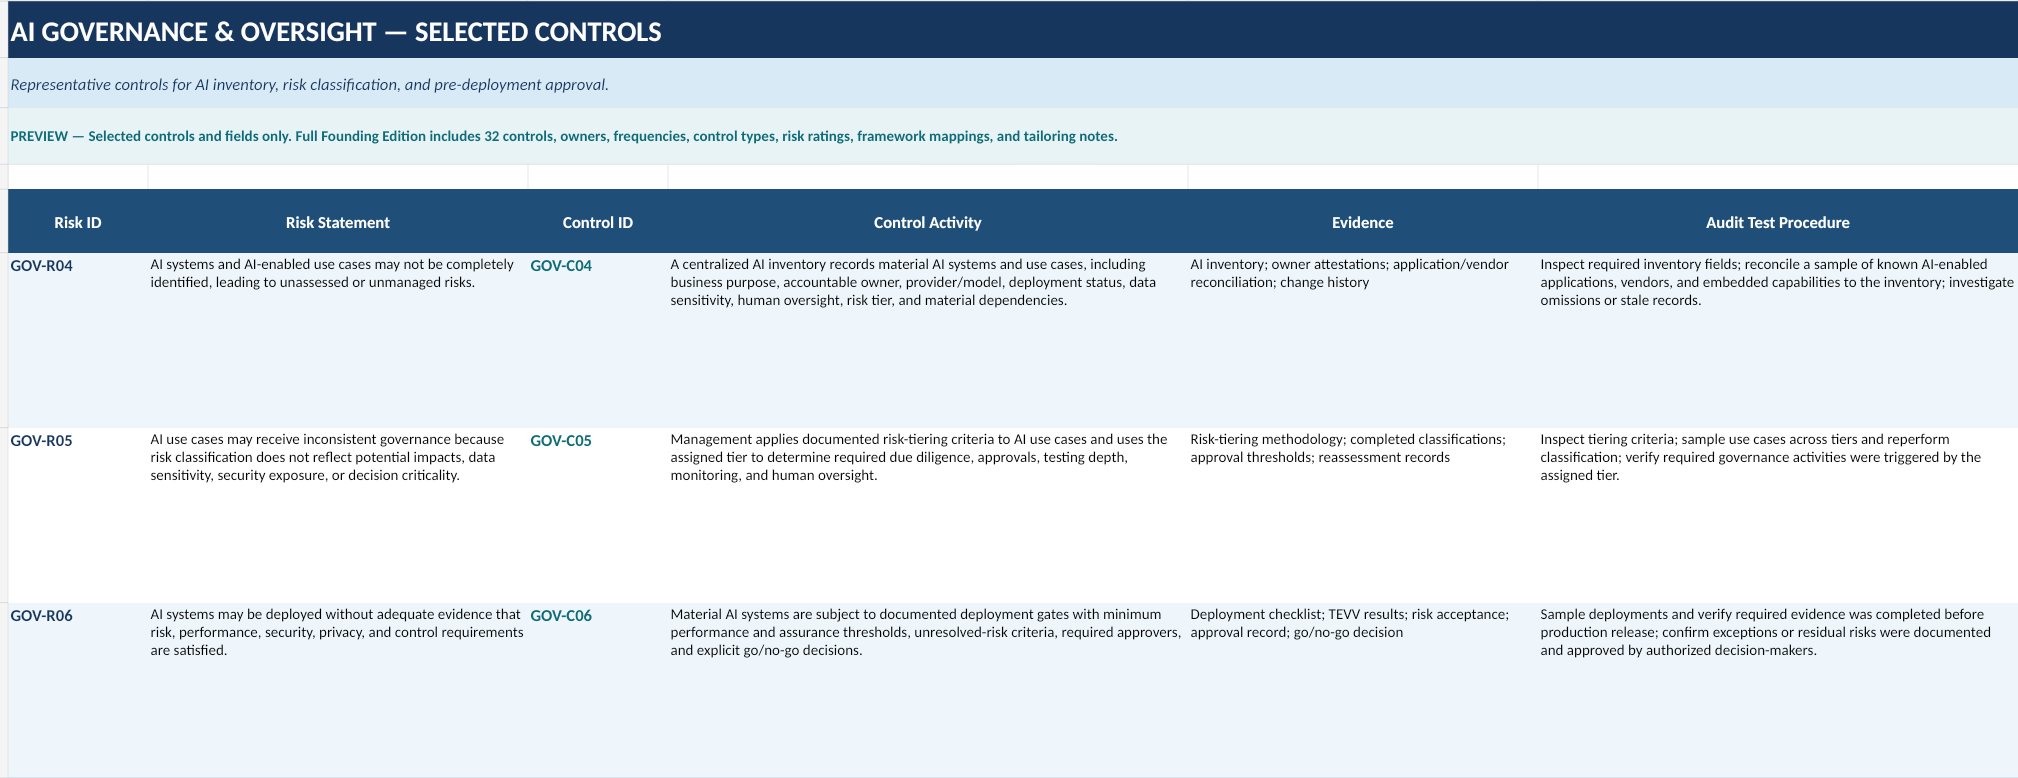 02
AI Governance & Oversight
Representative controls for AI inventory, risk classification, and pre-deployment approval.
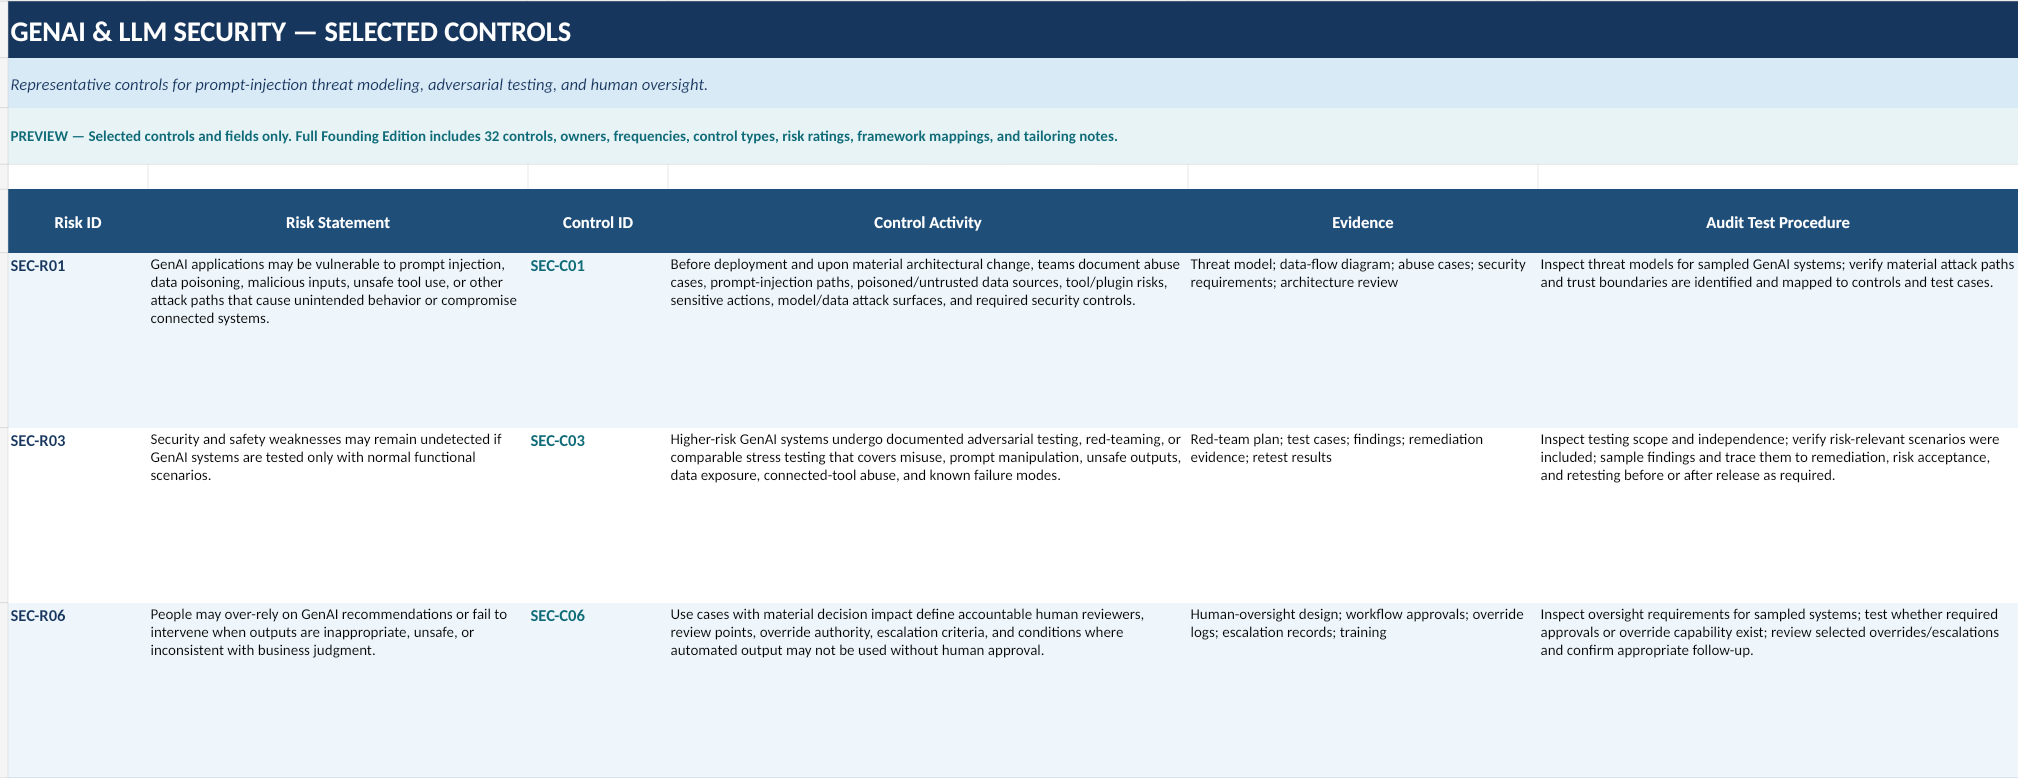 03
GenAI & LLM Security
Representative controls for prompt injection, adversarial testing, and human oversight.
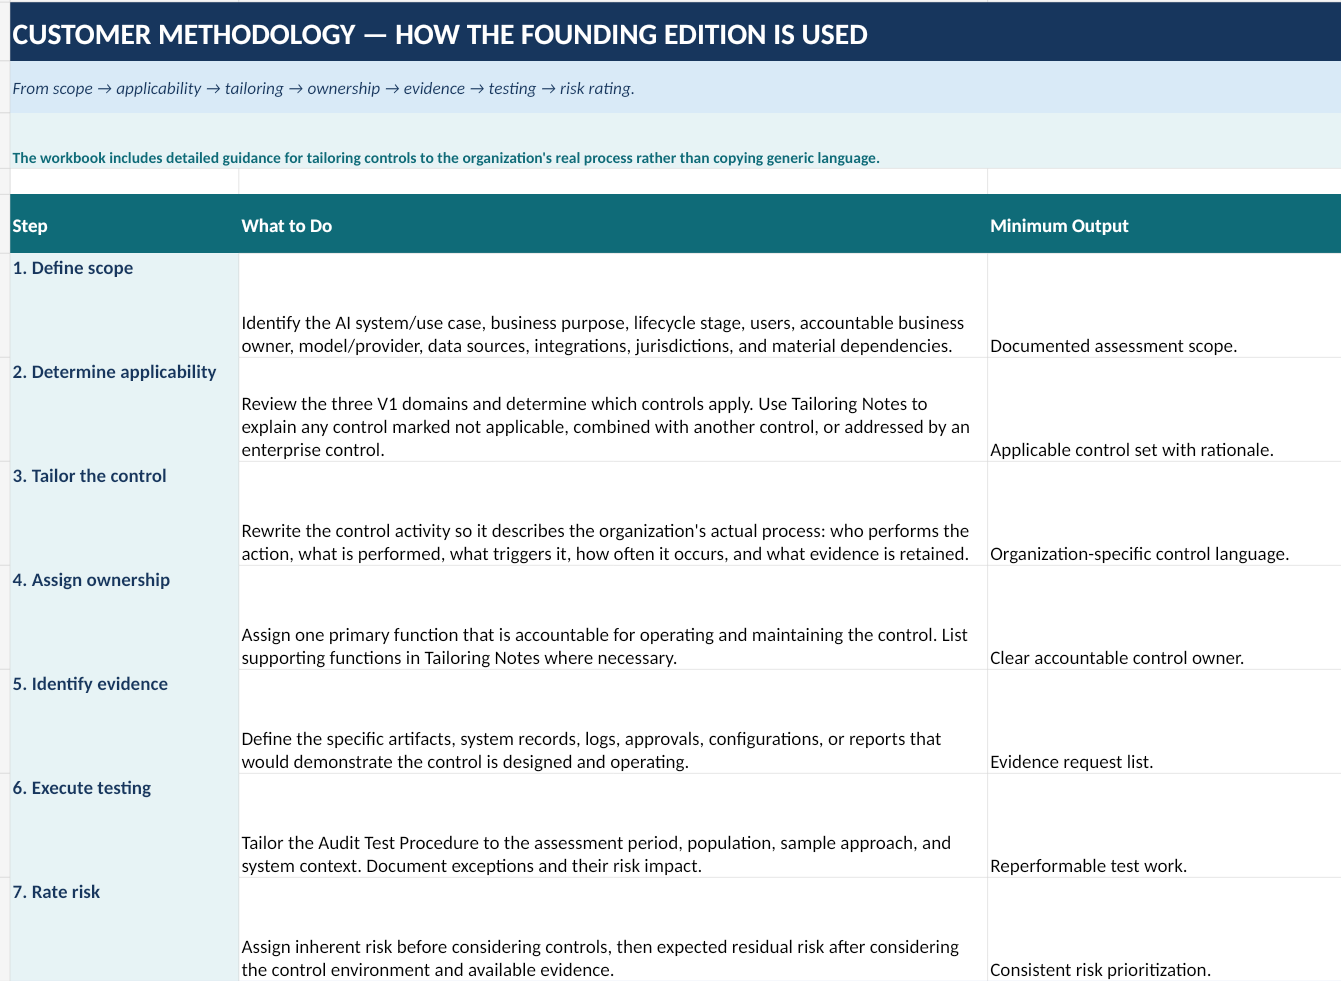 04
Customer Methodology
Scoping, tailoring, ownership, evidence, testing, and risk-rating guidance.
Built for Practitioners Responsible for AI Risk
Designed for IT Audit Managers and Directors, Technology Audit professionals, Internal Audit teams assessing emerging technology, Technology Risk professionals, AI Governance professionals, Compliance professionals, Enterprise Risk professionals with AI oversight, and GRC teams evaluating AI adoption.
About AI Governance Products
AI Governance Products develops practical tools that help audit, risk, compliance, and governance professionals translate AI frameworks into usable controls, assessments, and assurance procedures.
Our products are designed to help practitioners move from high-level guidance to structured, repeatable AI governance activities.
Practical. Actionable. Built for practitioners. Focused on real-world use.
Stop Building Your AI Risk & Control Matrix From a Blank Spreadsheet.
Start with a structured, practitioner-focused foundation and tailor it to your organization.
32 Controls | 3 Domains | Customer Methodology | Framework Mappings | Audit Testing Guidance
$79 — One-Time Purchase
Get the Founding Edition — $79Contact AI Governance Products
Questions about the Founding Edition, licensing, or product feedback? We welcome feedback from audit, risk, compliance, and AI governance professionals as the product continues to evolve.
Contact UsImportant Notice
AI Governance Products provides practical governance, risk, control, and assurance resources for professional use. The AI Governance Risk & Control Matrix — Founding Edition is intended as a practical starting point and does not constitute legal, regulatory, accounting, cybersecurity, or compliance advice. Use of this product does not represent or guarantee compliance, certification, conformity, or alignment with any specific law, regulation, framework, standard, or contractual requirement. Organizations should tailor control design, ownership, evidence requirements, testing procedures, risk ratings, and framework mappings based on their specific AI systems, business environment, industry, jurisdictions, regulatory obligations, policies, and risk tolerance.
License: Founding Edition v1.0 includes a single-purchaser internal-use license. The workbook may be used and tailored for the purchaser’s own professional or internal organizational purposes. It may not be resold, redistributed, published, sublicensed, or provided as a standalone product or template to third parties.